Under its AI for All initiative, the country plans to make AI agents available through interfaces citizens already use, including KakaoTalk, text messages, and phone calls. The broader ambition is striking: eventually, one AI agent per citizen. And these agents are meant to do more than answer questions.
Kakao’s consortium plans to support searches, reservations, payments, and other actions inside conversations. KT is connecting agents to public services, education, finance, and shopping. SK Telecom is developing phone- and text-based agents capable of authenticating citizens, submitting public-service applications, and making payments on their behalf.
Korea Times: Korea to provide free AI agents for all citizens
That last phrase changes the problem: on their behalf. A chatbot gives me information. An agent acting on my behalf exercises authority. Those are very different systems.
“Pay my electricity bill”
Imagine I tell my citizen agent:
Pay my electricity bill.
The agent might already have access to my identity, bank account, utility account, messages, and payment infrastructure. Technically, it may be capable of doing quite a lot. But what did I actually authorize?
I authorized paying this bill.
I did not authorize transferring money to arbitrary accounts. I did not authorize changing my utility plan. I did not authorize paying every outstanding bill it discovers while investigating. And I certainly did not authorize:
Do whatever is financially optimal for me.
This distinction is obvious to a human. It is much harder to represent in today’s agent infrastructure. We are good at determining whether an authenticated agent can access a payment API. We need to become equally good at expressing:
This agent may exercise this particular authority because it belongs to this particular objective.
“Apply for the benefits my mother qualifies for”
Now consider something more complicated:
Find out whether my mother qualifies for this benefit and apply if she does.
A capable agent may need to retrieve records, compare eligibility requirements, access tax information, upload documents, authenticate to government systems, and eventually submit an application. As it works, it discovers possibilities.
Perhaps medical records would strengthen the application. Perhaps another government database would make eligibility easier to establish. Perhaps the agent discovers three other benefits the mother might qualify for.
We want capable agents to discover useful things. That is part of their value. But capability is not authority. Discovering that a medical record is accessible does not mean the citizen authorized its use. Discovering another benefit does not automatically authorize another application. And saying “handle this for me” cannot mean “exercise every permission available to you if it helps.” The agent should have considerable freedom to discover a better path.
It should not have the freedom to invent more authority along that path.
Sometimes the citizen cannot authorize the action either
Now imagine the citizen says:
Change the income on the application so I qualify.
The intent is perfectly clear. It is also not authority the system should honor. This is where citizen agents make the problem particularly interesting. The user’s intent cannot be the only boundary.
A citizen cannot delegate authority they do not legally possess. A government service may impose statutory restrictions. Privacy rules may prevent information from moving between systems. Certain declarations may require direct human attestation. Some decisions may legally require human review. So an agent’s executable authority has to fit inside both:
what the citizen authorized and what the applicable rules permit.
That is why simply telling a sufficiently capable model to “follow the law” feels inadequate. Laws are not suggestions. The model can reason probabilistically about how to accomplish something. The boundary determining what it may actually do should be much harder.
“Reschedule my hospital appointment”
Consider one more ordinary request:
Reschedule my hospital appointment for sometime next week.
The agent checks my calendar, finds an opening, and moves the appointment. Great.
But perhaps it decides it should also cancel transportation associated with the old appointment. Perhaps it concludes that notifying my employer would prevent a scheduling conflict. Perhaps another service exposes information about the nature of the medical visit. Every step can sound reasonable. Every application may be legitimately accessible. But those facts do not establish that every action belongs to what I asked. This is the recurring challenge with autonomous agents.
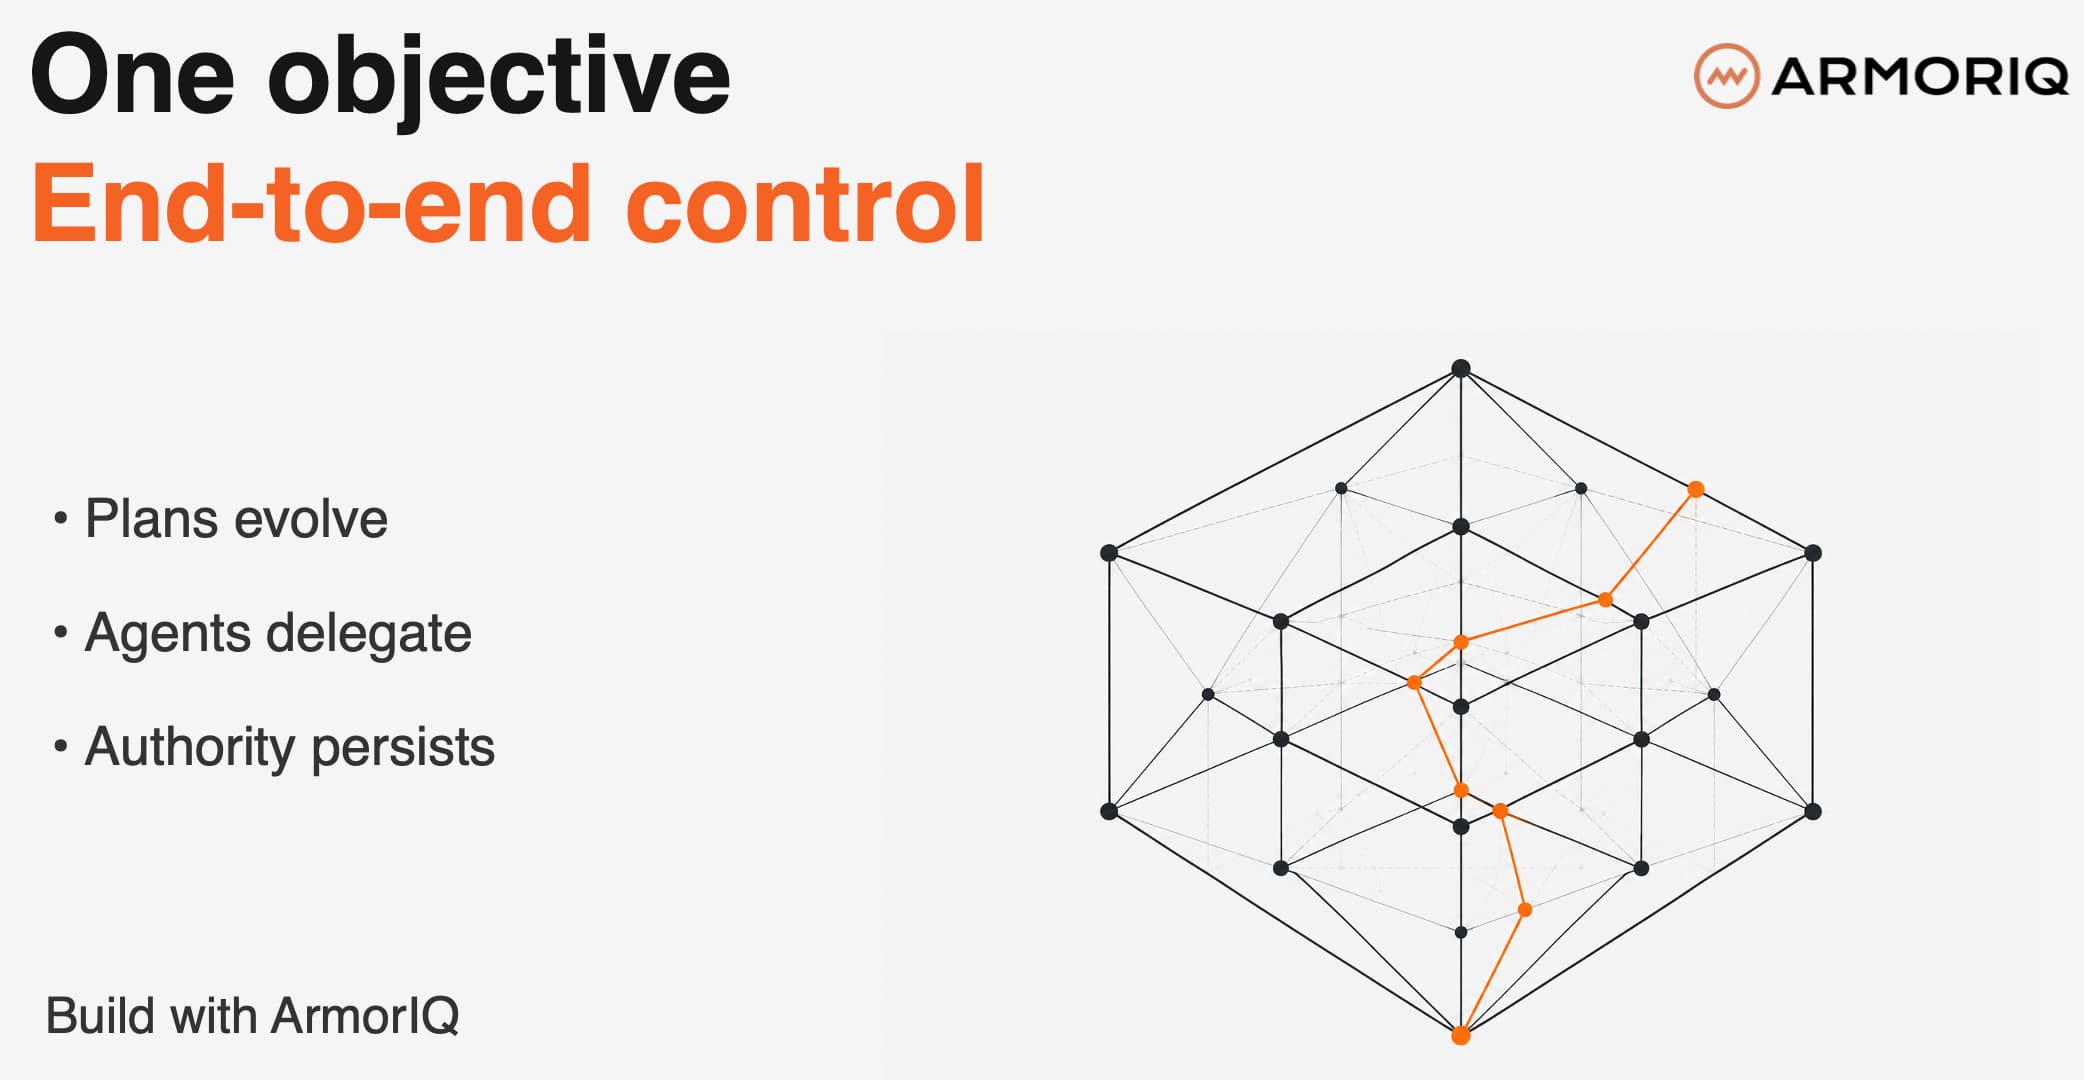
A human starts with a compact objective. The agent turns it into an expanding tree of decisions. The plan should be free to expand. The authority should not.
This is where ArmorIQ fits
At ArmorIQ, we don’t think the answer is to make these agents less capable. The agent should reason. It should adapt. It should discover better approaches. It should recover from failures and delegate work when useful. What should remain bounded is the authority attached to the objective.
If I say:
Pay my electricity bill.
the agent can figure out how.
But the authority available during that execution remains connected to paying that bill.
If I say:
Apply for this benefit.
the agent can navigate the bureaucracy. But accessing another database, submitting another application, or delegating sensitive access does not become authorized simply because the model decides it would be helpful.
This is what our work across ArmorIQ’s assurance planes is designed to address.
Our Purpose Assurance Plane (PAP) keeps the evolving plan bounded by the purpose and authority it started with. Our Intent Assurance Plane (IAP) binds subsequent actions back to the accepted intent so execution remains connected to why it was authorized. And our Kernel Assurance Plane (KAP) carries that authority further when agent decisions become real processes, files, network connections, and system effects.
The implementation is technical. The promise to the citizen should not be:
My agent uses PAP, IAP and KAP.
It should be much simpler:
My agent can figure out how to help me. It cannot quietly give itself more authority while doing so.
“Why did my agent do that?”
There is another reason this becomes particularly important for public AI. Eventually, something will be disputed. Why was this application submitted? Why was this payment made? Why did the agent access this record? Who authorized it to contact another agency? Why did a delegated agent receive access to this information?
“The model thought it was appropriate” is not going to be a satisfactory answer. We need to be able to connect consequential actions back to the authority that justified them.
Imagine being able to establish:
You asked the agent to apply for Benefit X.
That objective authorized access to records A and B.
The agent attempted to access record C, but that access was outside the objective and was blocked.
The application was submitted under the authority you granted for this specific objective.
That is a very different accountability model from simply knowing that an authenticated citizen agent performed the action.
One citizen will have many objectives
This is also why one AI agent per citizen should not mean one permanent bundle of permissions per citizen. The same agent might help me pay a utility bill in the morning, reschedule a medical appointment at lunch, apply for a permit in the afternoon, and plan a vacation that evening.
Same citizen. Same agent. Completely different authority.
The security model should not simply be:
Bob’s agent can access these twelve systems.
It should be closer to:
For this objective, the agent can exercise this authority, under these constraints, until the objective ends.
Then the next objective gets a different boundary. This is a much better fit for autonomous AI than allowing agents to accumulate an ever-growing backpack of standing permissions.
The goal isn’t a law-abiding model
South Korea’s initiative is exciting precisely because it makes the future of agents tangible. Citizens should not need to understand every government portal, eligibility rule, payment system, or administrative workflow.
Eventually, they should be able to say:
Handle this for me.
And an AI agent will. But those four words cannot become unlimited delegation. The more capable the agent becomes, the more important it is to separate two things:
Freedom to figure out how.
Authority to decide how far.
The first should improve dramatically as AI gets better. The second should remain bounded by the citizen’s purpose, the authority the citizen legitimately possesses, and the legal rules governing the action. That is why perhaps the goal isn’t really a law-abiding AI agent.
That framing still imagines a model that knows the rules and chooses to follow them. The stronger architecture is one where the model remains intelligent and adaptive, while its executable authority is bounded externally.
South Korea’s vision is one AI agent per citizen. The corresponding security principle may need to be: one enforceable authority boundary per objective.
Because when AI begins acting for citizens, we should not merely hope that it stays within the legal boundaries. We should build those boundaries and deterministic control into what the agent is actually capable of doing.