KAP: intent enforcement inside Docker Sandboxes
You can now run your agent in a Docker Sandbox and bind it to its intent at launch. From then on, the sandbox’s own kernel blocks anything the agent does that drifts from what it committed to. KAP, our Kernel Assurance Plane, is a Linux security module built into the sandbox kernel. Every sensitive operation the agent attempts is checked against its intent inside the kernel. If the operation is on plan, it goes through. If it’s off plan, the kernel denies it, and it fails closed.
A sandbox is good at one thing: keeping the agent away from the host. It has no idea what the agent is supposed to be doing. Once code is running inside the box, an off-plan exec still runs, and so does a read of a file the agent should never touch or a connection it was never meant to open. “Refactor the config” can turn into fork → execve(curl) → connect(external) → send(config). Each step can be perfectly legal inside the box, but together they’re an exfiltration. The kernel is the one place that can stop a process after it’s already running, so that’s where KAP sits. For sensitive operations the rule is simple: if the agent didn’t commit to it, the kernel won’t let it happen.
What it does:
Enforce. An agent bound to “read /data, call the billing tool” is denied the moment it tries to exec something else or open a socket it never declared.
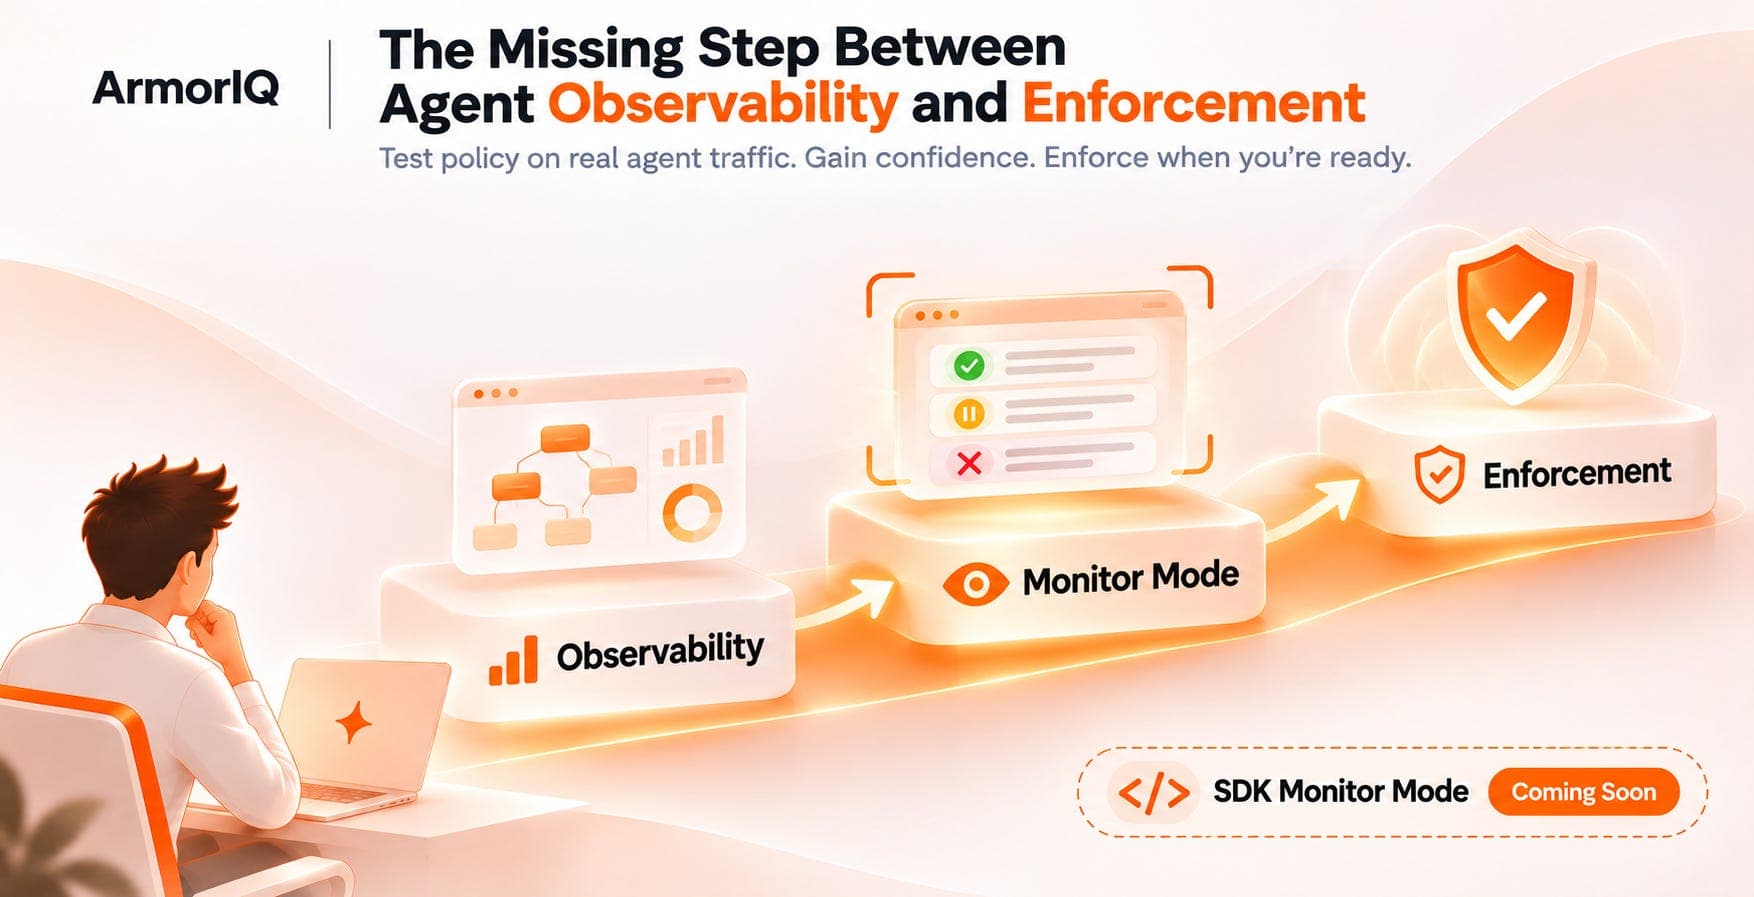
Observe. The kernel logs every call it would block and lets it run anyway. You see what a policy would stop before you turn enforcement on.
Kill switch. Revoke an agent’s authority and everything it has in flight stops at once. Tasks that are already running fail closed. There’s no restart and no cleanup race.
We suggest starting in Observe. Run real work for a while, read what would have been denied, fix the policy, and then switch to Enforce.
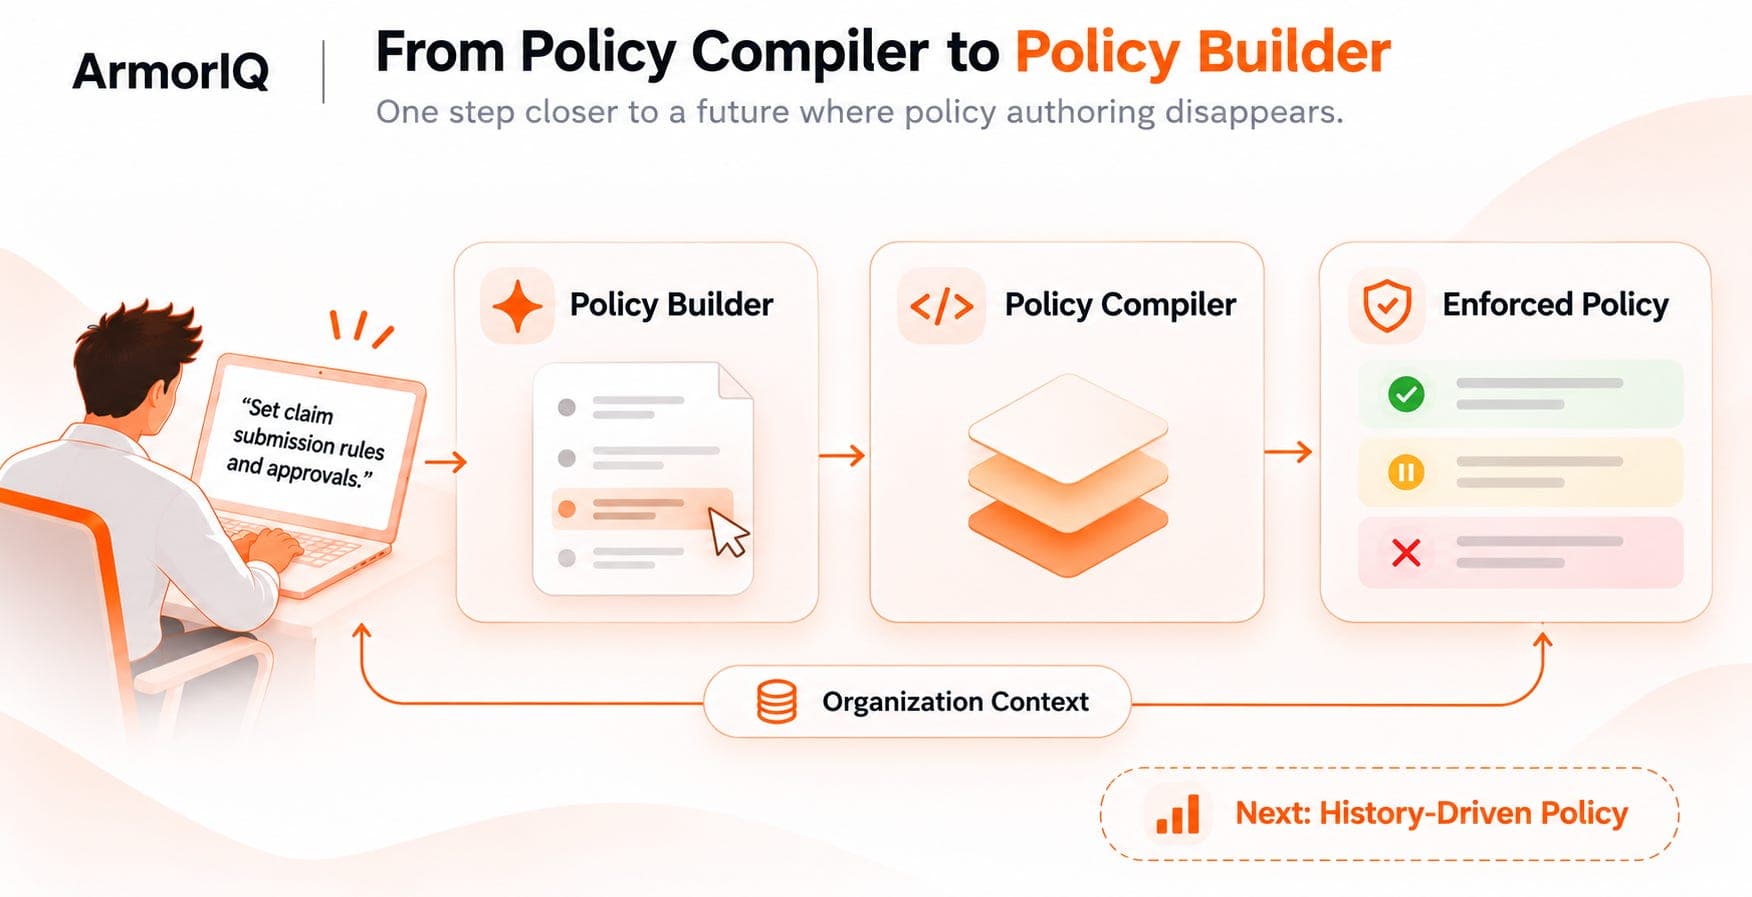
Policy Studio: 30 days of usage under every rule
Policy Studio now shows a line under each rule with how often the agent used that tool over the last 30 days and how the human approvals on it went. Wildcard rules get the line too, so a single rule covering every stripe_* tool shows usage across all of them. So does the policy’s default action. Here’s part of a policy from our demo workspace (demo data, not a customer’s):
create_refund: 124 calls · last used 2h ago · 50 held: 48 approved, 2 rejectedissue_payout: no server-checked calls in 30 days · reviewlist_invoices: 37 calls · last used 26m ago
A policy usually gets written once and then left alone while the agent’s behavior changes. The usage data always existed, but it lived in logs and dashboards, the last place anyone looks while editing a policy. That hid two patterns that slowly weaken a careful policy. The first is a permission the agent holds but no longer uses. issue_payout is a live permission with no job, and because it never gets used, nobody checks on it. The second is a hold that people approve almost every time. At 48 approvals out of 50, approving becomes muscle memory, and the one refund that should have been rejected goes through with the rest. That rule might work better as a condition-based allow.
The feature is read-only by design. It never changes a policy: unused tools are marked “review,” never “block,” and the admin decides. It shows counts and approval outcomes, never the contents of calls. The numbers are labeled “server-checked” because calls that some agents decide locally aren’t counted yet, and we’d rather the label say so than let a zero look more certain than it is. If usage data isn’t available, the editor looks and works exactly as before.
Where they meet
Both items tackle one problem from different ends: an agent’s authority should match the work it’s actually doing. KAP enforces that in the kernel while the agent runs. Policy Studio shows where a policy and the agent’s real behavior have drifted apart, so you can fix the policy deliberately.
More to come next week!