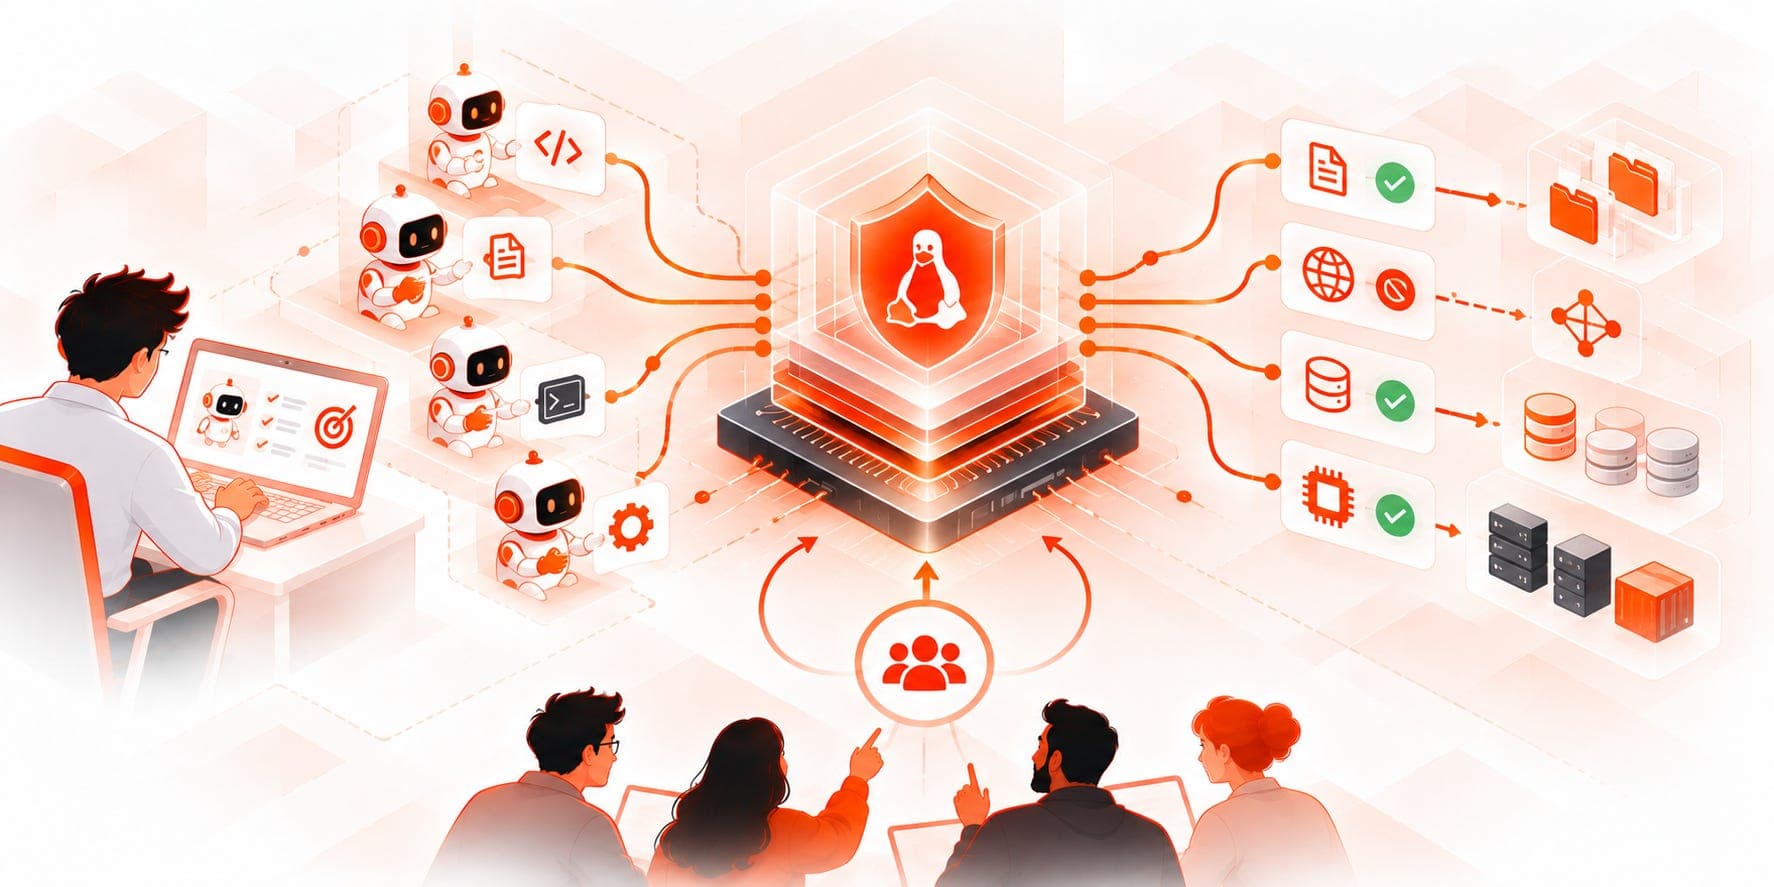
AI agents are becoming autonomous operators. The systems they run on were not designed to understand the objectives behind their actions.
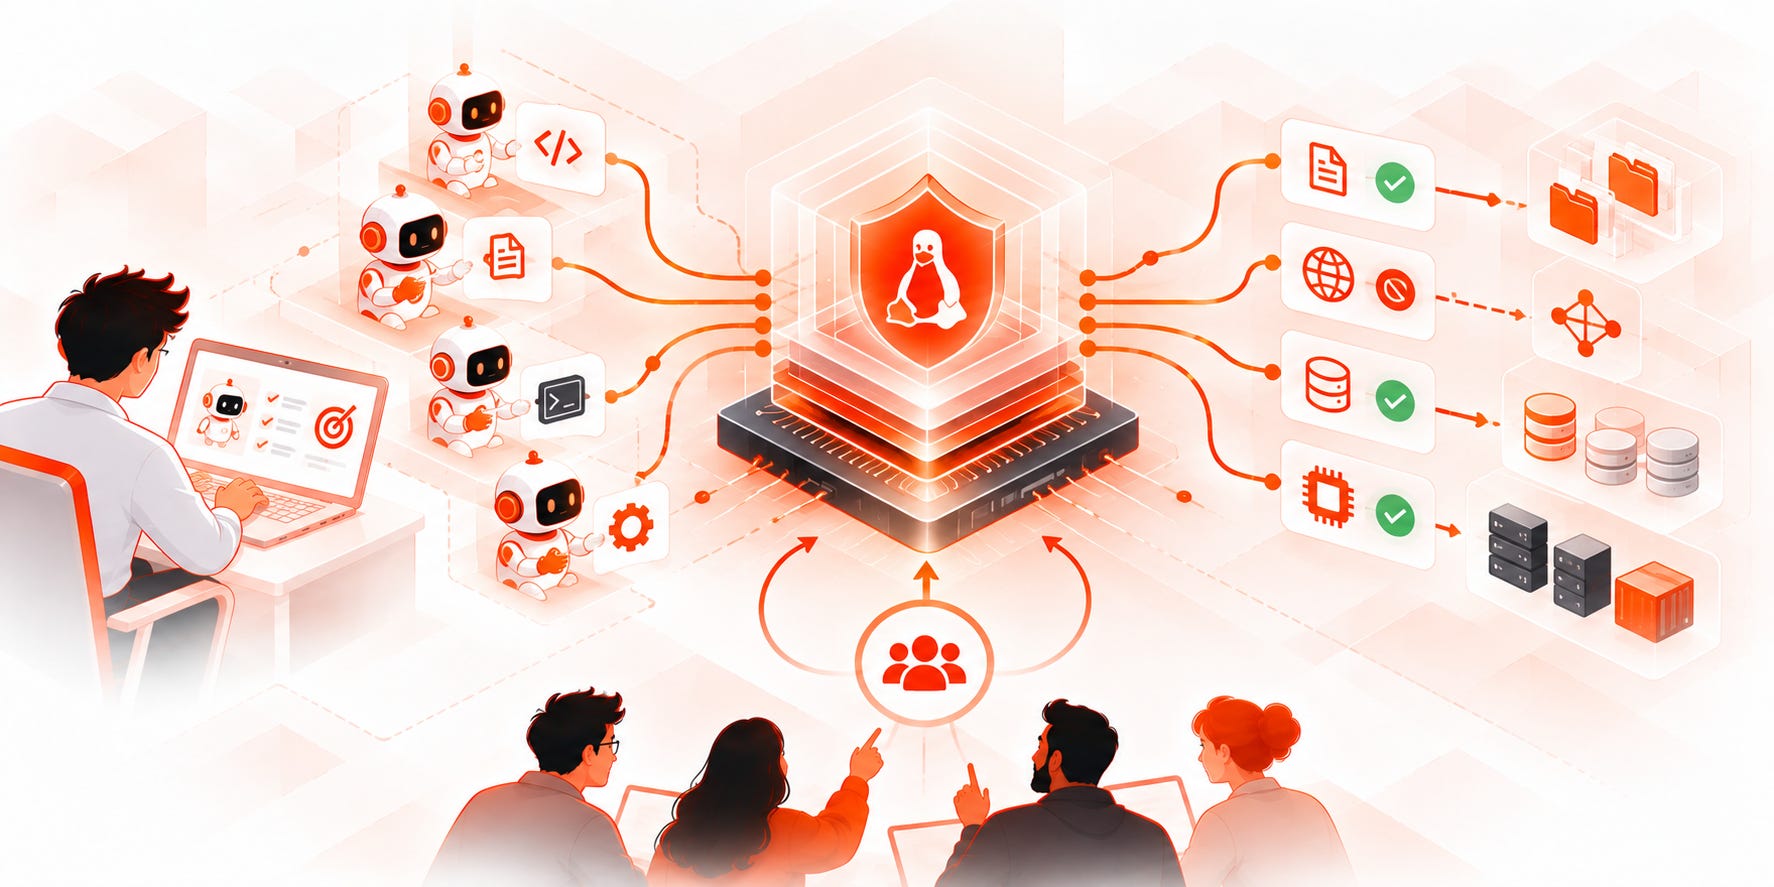
Today, we’re taking a step toward changing that. At ArmorIQ, we’ve submitted a six-patch series introducing the Kernel Assurance Plane (KAP) to the Linux Security Module (LSM) community. KAP proposes a new kernel abstraction called Intent Lineage Groups (igroups), designed to bind executable authority to the objective an agent is carrying out and enforce that authority as execution evolves.
We believe this could become a foundational primitive for agent runtime frameworks, much as cgroups became foundational to modern container infrastructure. But building such a primitive requires more than one company.
We’re inviting Linux kernel developers, security researchers, container-runtime maintainers, and agent runtime framework builders to review, challenge, and contribute to this work.
Review the Linux KAP patch series
Why Existing Agent Security Approaches Fall Short
Most approaches to securing AI agents focus on controlling tools, APIs, or execution environments.
Tool-based policies determine which tools an agent can invoke. Agent runtime frameworks introduce approval gates and policy checks. Sandboxes constrain filesystem, network, and process access. These are necessary controls. But they do not automatically preserve the authority of an objective throughout execution.
Consider an agent authorized to install dependencies and run tests. It invokes a shell, launches subprocesses, downloads packages, and generates scripts. Once dependencies are installed, network access should no longer be necessary. Yet a previously launched subprocess may continue running with network access. The tool invocation was authorized. The sandbox was never breached. Every system call may be individually legal.
But the authority to make that network connection should no longer exist.
This exposes a fundamental gap. Agent runtime frameworks understand objectives, but cannot necessarily enforce every downstream system operation. The operating system enforces operations, but does not know which objective authorized them or whether that authority has since changed. And ultimately, every agent action that affects the local system is realized through operating-system mechanisms: processes, files, sockets, credentials, namespaces, and other kernel-managed resources.
We cannot build reliable intent enforcement solely at the tool boundary when execution continues beyond that boundary.
The cgroups Moment for Agentic Computing?
There is a useful parallel in the history of Linux containers. Before common kernel primitives became widely adopted, resource management and process isolation required substantial runtime-specific machinery. Linux cgroups provided a shared mechanism for organizing processes and governing resource consumption. Together with namespaces and other Linux primitives, they helped make modern container runtimes possible. Different runtimes could innovate independently while relying on common kernel-enforced foundations.
We believe agentic computing needs a similar abstraction for executable authority.
Where cgroups govern resource consumption, igroups aim to govern objective-scoped authority across execution lineage. An igroup associates execution with the authority established for a particular objective. That authority follows the task and its descendants, while changes and revocation become explicit system-level operations. The kernel does not need to interpret prompts or reason about human intent. That belongs in userspace. Instead, the kernel enforces the concrete authority derived from that intent, using existing Linux security mechanisms.
This separation is important: agent runtime frameworks remain free to implement their own planning, policy, and delegation models while relying on a common enforcement foundation.
What We’ve Contributed
Our October 28 RFC patch series introduces the initial implementation of KAP, including:
Intent Lineage Groups (igroups): A kernel abstraction for associating tasks and their descendants with objective-scoped authority.
KAP Linux Security Module: Enforcement of compiled authority through Linux security hooks.
securityfs control plane: Interfaces for creating igroups, binding tasks, and managing authority.
Authority epochs and revocation: Mechanisms for invalidating previously authorized execution.
Namespace transition checks: Additional enforcement for
unshare()andsetns().
The implementation builds on existing Linux security infrastructure rather than attempting to introduce semantic reasoning into the kernel. An earlier version has also been exercised inside Kata microVMs, providing an initial basis for evaluating enforcement overhead and integration.
This is still an RFC, not a finished or accepted Linux subsystem. Important work remains around concurrency, lifecycle management, testing, performance, and the appropriate upstream architecture.
We want the community involved in those decisions.
A Call to the Systems Community
Our goal is not to make KAP an ArmorIQ-specific enforcement mechanism.
Our goal is to help establish interoperable, objective-scoped enforcement that different agent runtime frameworks can build upon.
That requires a shared discussion about where authority should live, how it should propagate, and how it should be revoked.
We are particularly looking for contributions around:
Linux kernel architecture: igroup lifecycle, LSM integration, concurrency, security boundaries, and compatibility with existing mechanisms.
Agent runtime integration: Mapping objectives, delegated tasks, and changing authority into kernel-enforceable state.
Security evaluation: Adversarial workloads, authority leakage, stale execution, revocation, and bypass testing.
Performance and interoperability: Benchmarking, selftests, and integration with container and agent runtimes.
We welcome criticism of the design as much as contributions to the implementation. If existing Linux mechanisms can provide a better foundation, that discussion is equally valuable. The larger question is worth answering together:
Can we give agent runtime frameworks a common OS-level primitive for enforcing objective-scoped authority, just as container runtimes gained common primitives for resource governance and isolation?
We believe the answer should be yes. And we’ve submitted the first patches to start that conversation.
Read the RFC. Review the code. Challenge the assumptions. Contribute.
Kernel Assurance Plane: Linux Patch Series
ArmorIQ | Secure Intent. Assure Autonomy.